The unified platform for Self-Assessment & Third-Party Risk Management
Conduct comprehensive DPDP Act 2023 privacy self-assessments, manage organizational risks, and audit third-party data processors and vendors — all from one console.
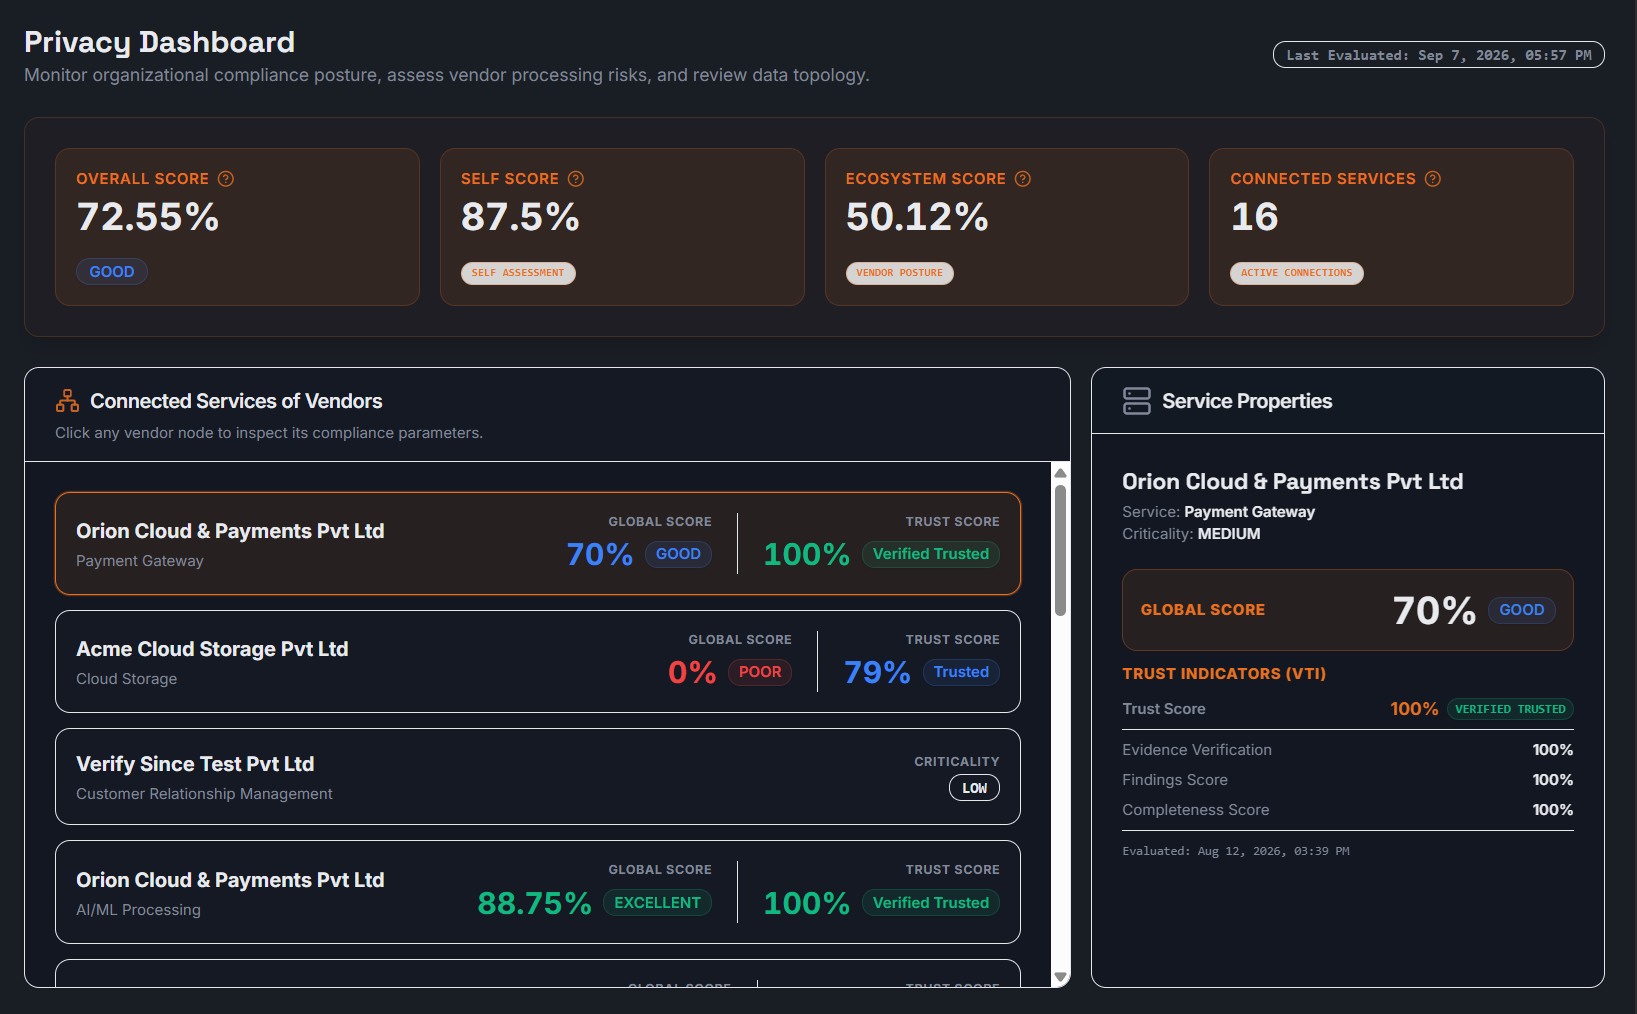
Two powerful assessment modules in one platform
While other vendors sell separate tools, PATM unifies internal self-assessment and risk governance with external third-party risk management into a single DPO command center.
Self Assessment and Risk Management
Evaluate internal data processing activities, diagnose privacy compliance gaps, conduct fiduciary self-assessments, and manage enterprise risk posture under India's DPDP Act 2023.
- Statutory DPDP Act 2023 self-assessment questionnaire frameworks
- Internal data processing risk mapping & gap diagnosis
- Severity × Likelihood risk matrix with automated impact scoring
- Internal remediation tracking & corrective action workflows
Third Party Risk Management (TPRM)
Audit third-party vendors and data processors across your entire supply chain with continuous risk tiering, evidence verification, and remediation tracking.
- Section 8(2) DPDP compliant data processor evaluations
- Dedicated vendor response portal with zero-cost access
- Option-aware evidence vault with tamper-evident audit logs
- Vendor compliance scorecards, risk tiers & remediation workflows
End-to-end self-assessment & third-party risk management
From internal privacy gap analysis to vendor audit certification — fully automated.
Fiduciary Self-Assessment
Conduct structured self-assessments to detect internal compliance gaps, data processing risks, and mitigation priorities under DPDP Act 2023.
Third-Party Vendor Risk (TPRM)
Evaluate data processors and vendors with automated assessment dispatch, tokenized portal access, and continuous risk monitoring.
DPDP 2023 Ready Frameworks
Pre-loaded questionnaire frameworks for both internal fiduciary self-assessment and external third-party compliance evaluations.
Option-Aware Evidence Vault
Require evidence attachments per question or specific option with full validation and tamper-evident audit logging.
Automated Risk Matrix
Calculate organizational and vendor risk grades (Severity × Likelihood) automatically upon assessment submission.
Audit-Grade DPO Reports
Export single-click compliance scorecards, internal audit dossiers, executive PDFs, and tamper-proof logs for regulators.
From risk evaluation to audit-ready in 6 steps
A unified workflow designed for Data Protection Officers (DPOs), risk leads, and governance teams.
Comprehensive privacy self-assessment & gap diagnosis
Evaluate internal data handling, consent mechanisms, notice compliance, and security safeguards against statutory DPDP requirements.
- Structured questions covering DPDP Act 2023 principles
- Real-time compliance gap identification
- Section-by-section progress & draft auto-saving
- Immediate organizational risk baseline calculation
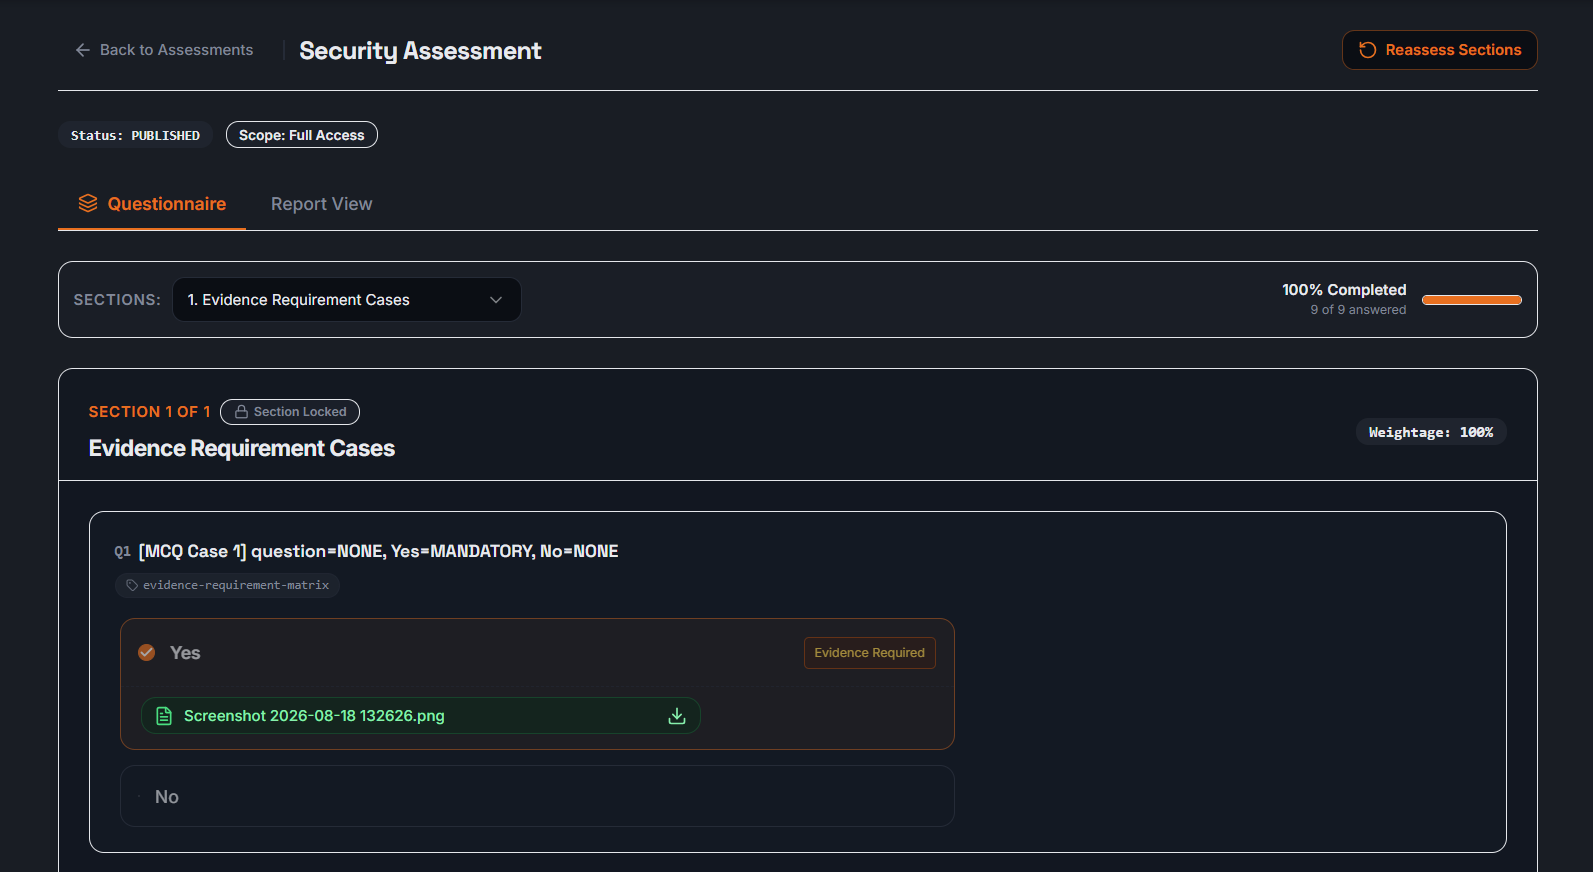
Unified inventory of third-party vendors & data processors
Maintain a single command center tracking third-party data processors, vendors, and supply-chain risk profiles under the DPDP Act 2023.
- Categorized by risk level (Low, Medium, High)
- Data processor vs service vendor classification
- Real-time assessment status & DPO review stage
- Centralized asset, vendor & DPO contact mapping
Dispatch vendor evaluations or run internal assessments
Invite third-party vendors to a secure, passwordless portal or assign internal departments self-assessment modules.
- Pre-configured vendor security & internal audit templates
- Dedicated vendor portal with passwordless access
- Custom submission deadlines & reminder schedules
- Multi-collaborator response workflow
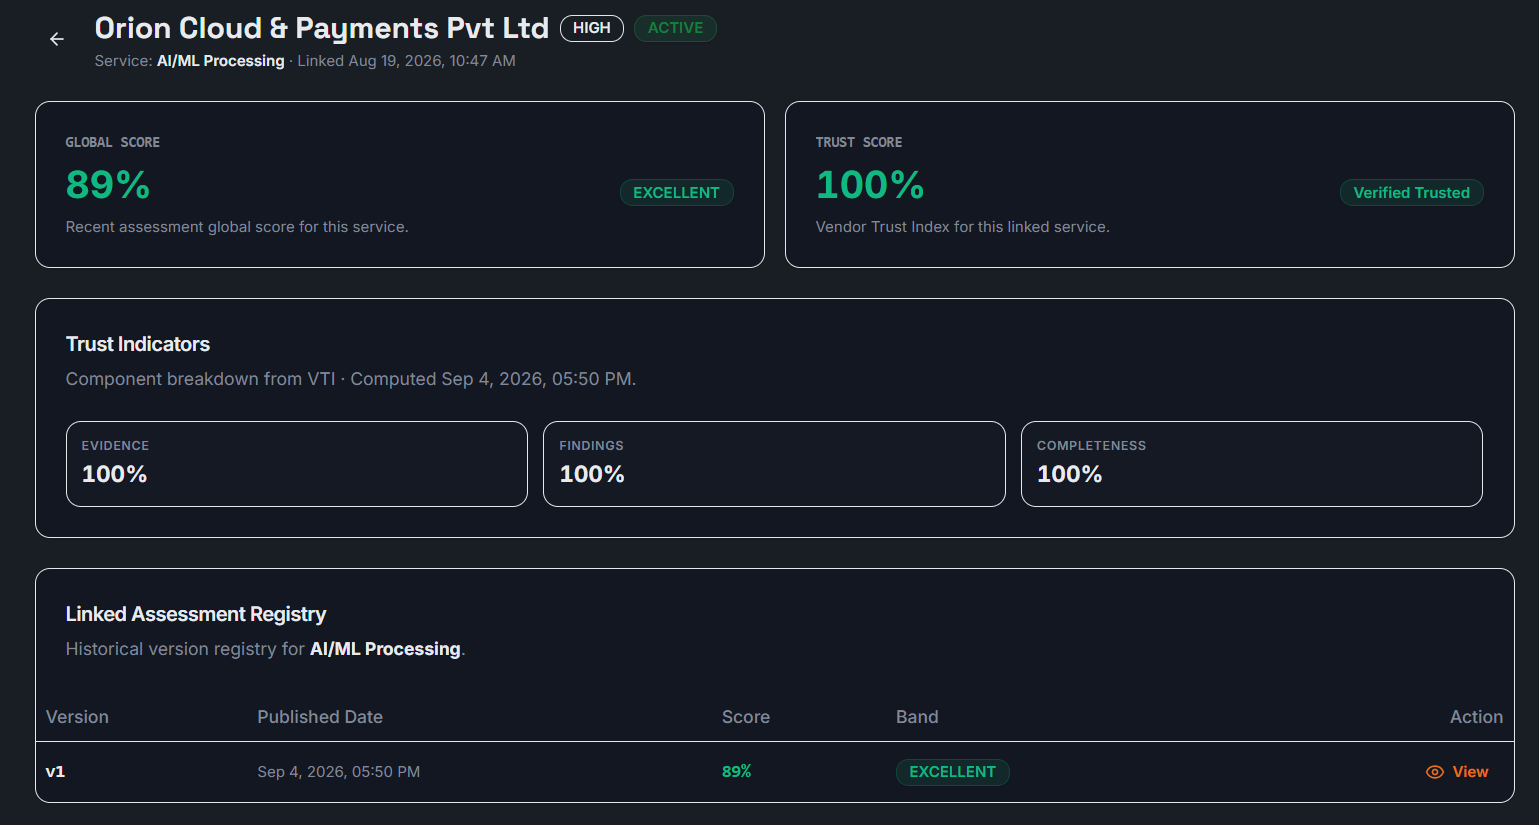
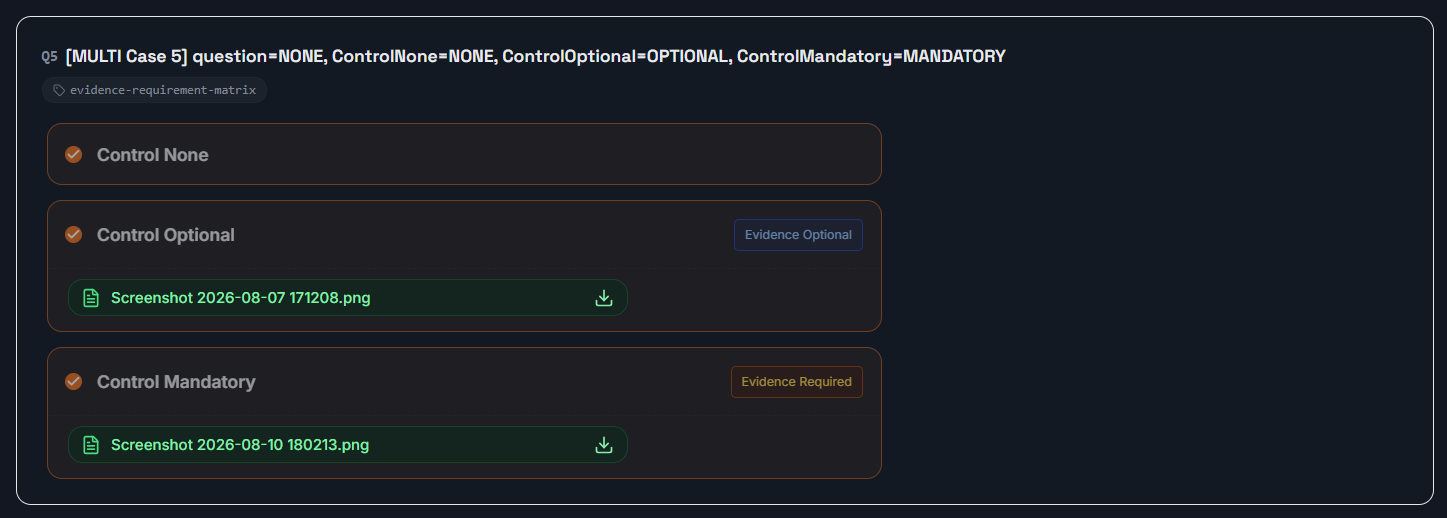
Option-aware evidence verification & audit trail
Verify certificates, SOC 2 reports, ISO certifications, and security policies attached directly to specific options or questions.
- Option-specific evidence mapping
- Inline file inspection & download controls
- Evidence replacement & version tracking
- Tamper-evident hash verification records
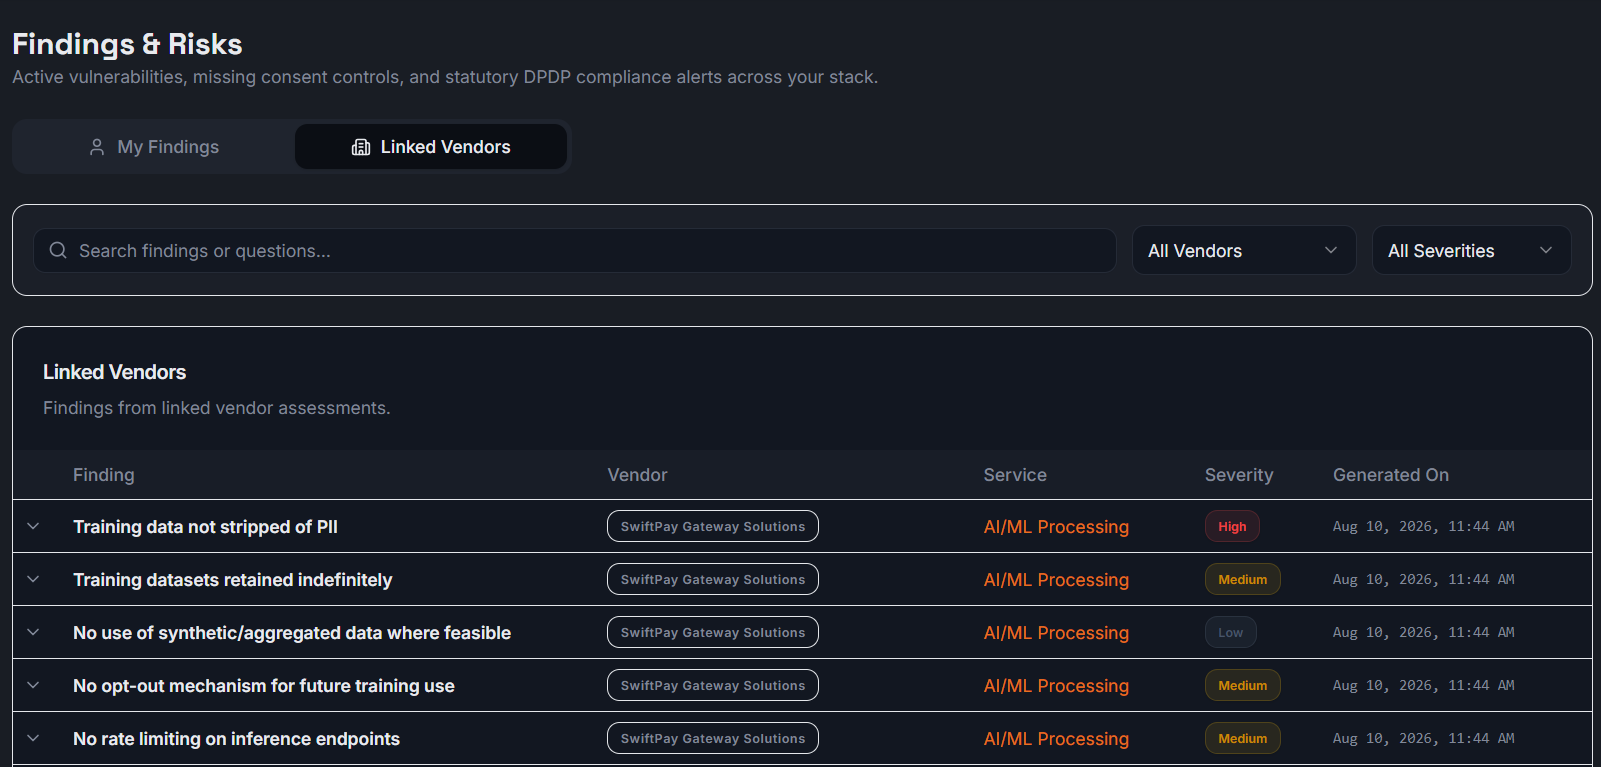
Address internal risk gaps & vendor non-conformities
Identify security gaps and compliance non-conformities across self-assessments and vendor evaluations, assigning remediation action items until resolution.
- Automated risk gap identification
- Mitigation task assignment & vendor revision requests
- Target completion dates & escalation alerts
- Audit log of DPO resolution approval
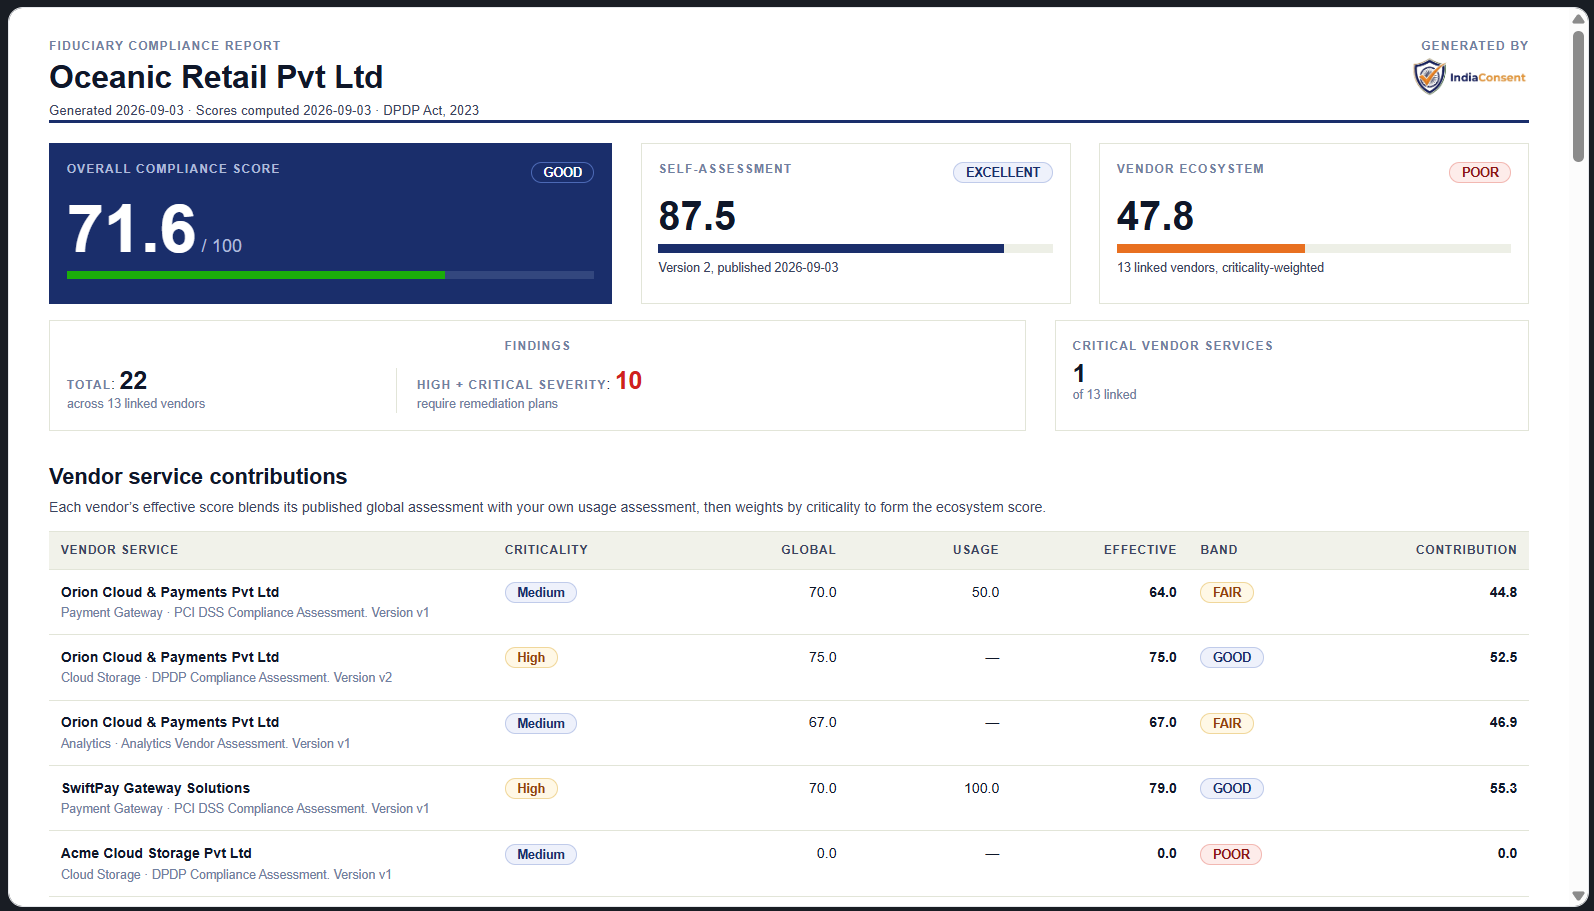
Single-click DPO compliance dossiers & certificates
Generate executive risk heatmaps, vendor compliance scorecards, and regulator-ready audit reports to prove continuous compliance.
- Executive DPO compliance scorecards
- Vendor risk tier heatmaps & category breakdowns
- DPDP 2023 data fiduciary audit dossiers
- Timestamped event logs & hash integrity checks
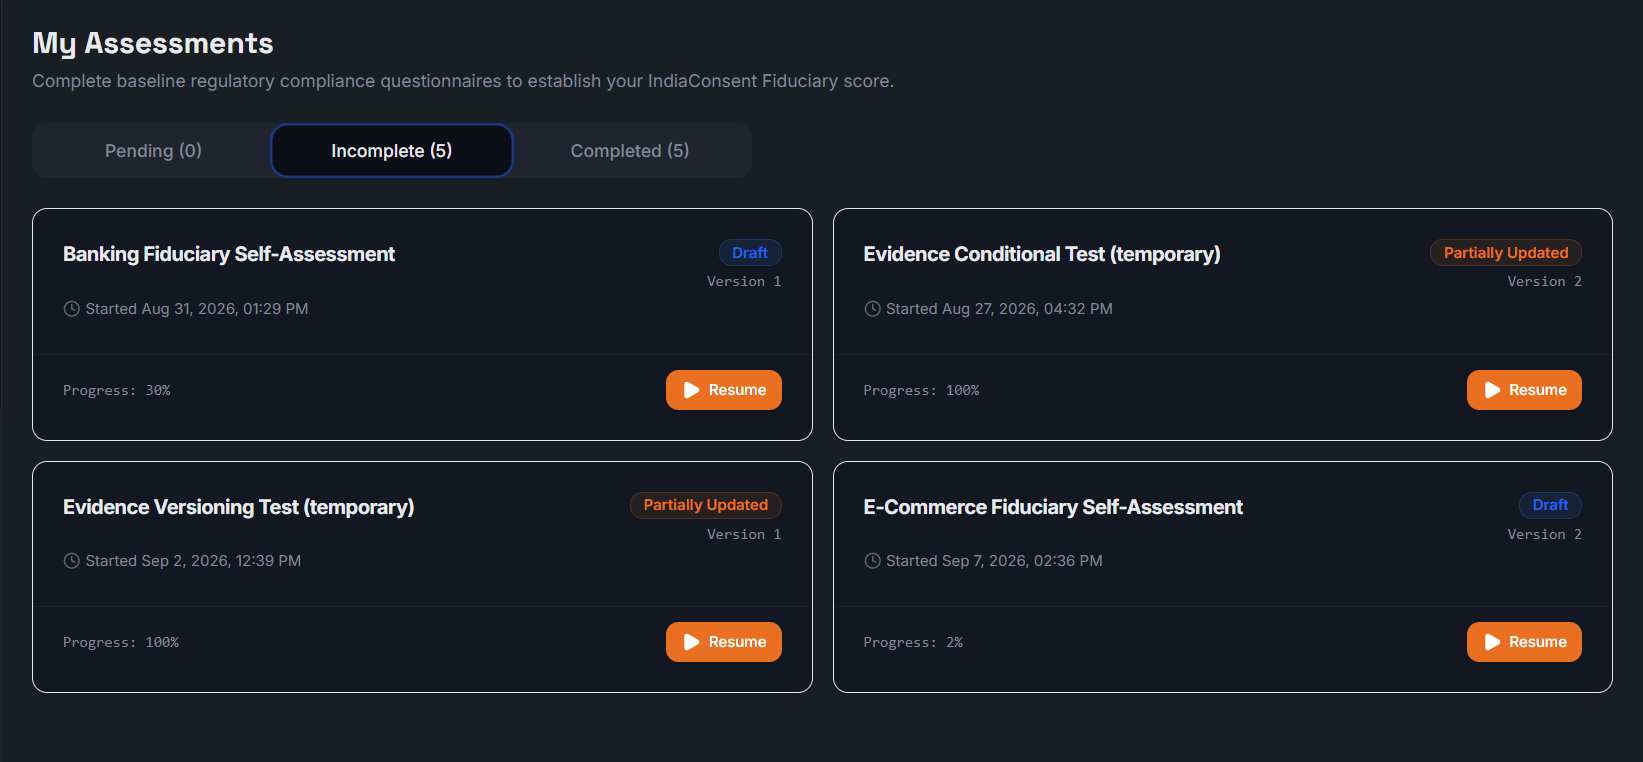
Conduct structured internal privacy assessments & data processing evaluations.
Audit data processors & vendors with automated dispatch portals.
Option-aware evidence attachments with tamper-evident audit logs.
Calculate privacy impact scores & risk grades instantly.
Assign finding action items and mitigation tasks to resolution.
Single-click export of internal compliance dossiers & vendor audit logs.
Questions, answered
How do Self-Assessment and Third-Party Risk Management (TPRM) work together?
Self-Assessment allows Data Fiduciaries to evaluate their own internal processing activities, identify privacy gaps, and establish baseline compliance under the DPDP Act 2023. Third-Party Risk Management (TPRM) extends this governance externally to all data processors and vendors handling personal data on behalf of the fiduciary, satisfying Section 8(2) obligations. Both tracks operate seamlessly within the same unified console.
What frameworks are included for internal Self-Assessment?
PATM includes pre-configured self-assessment frameworks aligned with India's DPDP Act 2023 provisions — covering lawful basis of processing, notice mechanisms, data principal rights workflows, security safeguards, and breach readiness.
Do third-party vendors need a paid subscription to respond?
No. Third-party vendors receive secure, role-based portal access to complete assessments, upload required option-level evidence, and collaborate on remediation at zero cost.
How does option-aware evidence verification work?
When an assessment respondent selects a specific compliance option (e.g. 'Certified under ISO 27001'), PATM dynamically requires evidence attached explicitly to that option, logging immutable file audit records.
Elevate your privacy & vendor risk management today
Run internal self-assessments, manage organizational risks, audit third-party data processors, and satisfy DPDP regulatory mandates with confidence.