The unified platform for Statutory Grievance Redressal & DPO Operations
Empower Data Principals to exercise privacy rights, triage concerns through a collaborative officer workspace, track statutory Rule 14 SLAs, and prevent Data Protection Board escalations.
End-to-end architecture from citizen complaint to DPO resolution
A unified system built for frictionless citizen access, deep officer investigations, and statutory DPO compliance.
Citizen Privacy Rights Portal
Empower Data Principals with an accessible, transparent self-service interface to submit privacy grievances across 12 statutory categories, view live timelines, and supply requested clarifications.
- 12 Pre-configured DPDP categories (consent withdrawal, erasure, correction, etc.)
- Direct linkage with consent notices and evidence file uploads
- Real-time transparent progress tracking with milestone events
- Two-way clarification replies and grievance reopen options
Officer Investigation Workspace
Equip designated Grievance Officers with a dedicated command desk to inspect case facts, maintain confidential internal notes, request supplementary evidence, and formulate defensible resolutions.
- Consolidated case facts card with verified identity & consent tags
- Structured 'Awaiting Info' question loop with citizen file exchange
- Confidential internal officer notes hidden from citizen view
- Formal resolution grounds logging and closure communications
DPO Oversight & Escalations
Provide Data Protection Officers (DPOs) and Org Admins with executive oversight of SLA countdowns, queue bottlenecks, near-breach alarms, and board-ready compliance audit dossiers.
- Rule 14 SLA countdown monitors with near-breach warnings
- Officer reassignment and senior supervisor escalation desks
- Analytics on average turnaround, category distribution & officer load
- Tamper-evident audit logs and compliance dossiers for regulators
Two Critical Rules Every DPO Must Enforce
Under DPDP Rule 14, unaddressed grievances escalate directly to the Data Protection Board. IndiaConsent provides the legal buffer and technical workflow.
The Rule 14 SLA Clock
Statutory countdowns before regulatory escalation
When a Data Principal registers a concern, strict statutory countdowns begin. If your organization fails to provide an effective, transparent resolution within prescribed limits, the citizen holds the legal right under Section 13 to petition the Data Protection Board.
Cryptographic Intake & Acknowledgment
Immediate timestamped acknowledgment with a unique tracking ID issued to the Data Principal, logging evidence hashes on immutable records.
Officer Triage & Clarification Loop
Grievance Officer inspects case facts, verifies consent notices, and opens a structured 2-way inquiry loop without dropping the ticket.
Defensible Resolution & Audit Dossier
Formal closure grounds recorded, citizen satisfaction confirmed with reopen rights, and an immutable compliance dossier compiled for the Board.
Statutory non-compliance penalty: Direct DPB complaints risk penalties up to ₹250 Crore under DPDP Act Section 33 per incident.
Tri-Party Architecture
Internal redressal preempts external Board intervention
Under the DPDP framework, IndiaConsent sits as a verifiable, neutral layer providing direct rights-exercise mechanisms to Data Principals while giving your Grievance Officers and DPOs the tools to resolve disputes defensibly.
Data Principal (Citizen)
Lodge Concern • Two-Way Reply • Reopen
Statutory Intermediary
IndiaConsent Grievance Engine
SLA Timers • Audit Chronology • Ticket Dispatch
Data Fiduciary (Enterprise)
Grievance Officer Workspace & DPO Escalations
Readily accessible, multi-lingual intake mechanism published on all digital properties (Rule 14)
Designated, India-based Grievance Officer details visibly published to Data Principals
Statutory resolution timeframes enforced before citizens may escalate to the Data Protection Board
Complete, tamper-evident audit records maintained for regulatory inspection and legal admissibility
Purpose-built for Indian DPDP Act 2023 Rule 14 mandates
From automated SLA countdowns to defensible regulatory dossiers — fully structured.
DPDP Act Rule 14 Compliance
Built ground-up to satisfy statutory grievance redressal duties, providing accessible reporting, structured acknowledgment, and defensible resolutions.
Automated SLA Clocks
Pre-configured resolution timers dynamically track countdowns per category and trigger proactive escalation alerts before statutory deadlines lapse.
12 Statutory Complaint Categories
Pre-mapped taxonomy covering consent withdrawal, unauthorized processing, data deletion, breach alerts, and third-party data sharing restrictions.
Two-Way Citizen Clarifications
Send formal information requests to citizens when additional facts or proof are needed, pausing SLAs without prematurely closing tickets.
Multi-Role Delegation
Separate duties cleanly between frontline Grievance Officers investigating cases, DPOs supervising escalations, and Organization Admins managing teams.
Tamper-Evident Audit Trails
Every status transition, internal note, file upload, and officer assignment is recorded immutably to produce defensible dossiers for the Data Protection Board.
From complaint intake to defensible resolution in 6 steps
A transparent workflow uniting Data Principals, Grievance Officers, and DPOs.
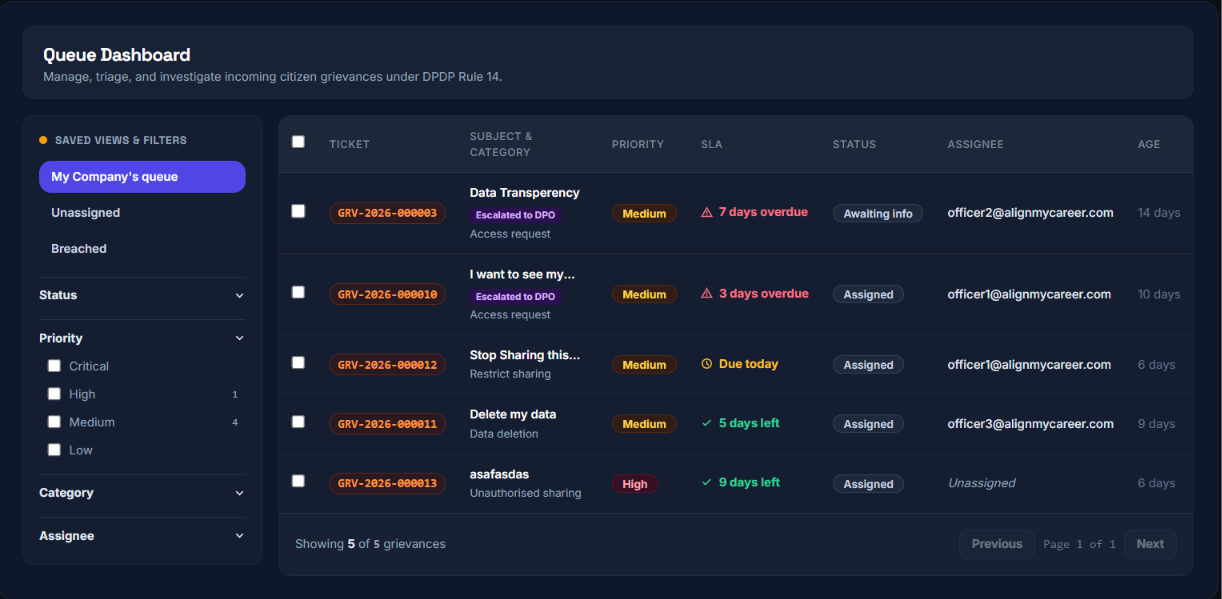
Frictionless lodging across 12 statutory privacy categories
Data Principals lodge privacy complaints using structured, accessible prompts with optional consent verification and supporting document uploads.
- 12 statutory privacy categories (consent withdrawal, erasure, correction, etc.)
- Direct linking of consent artifact and fiduciary identity
- Secure document attachments with strict size & MIME validation
- Instant ticket generation with trackable reference ID
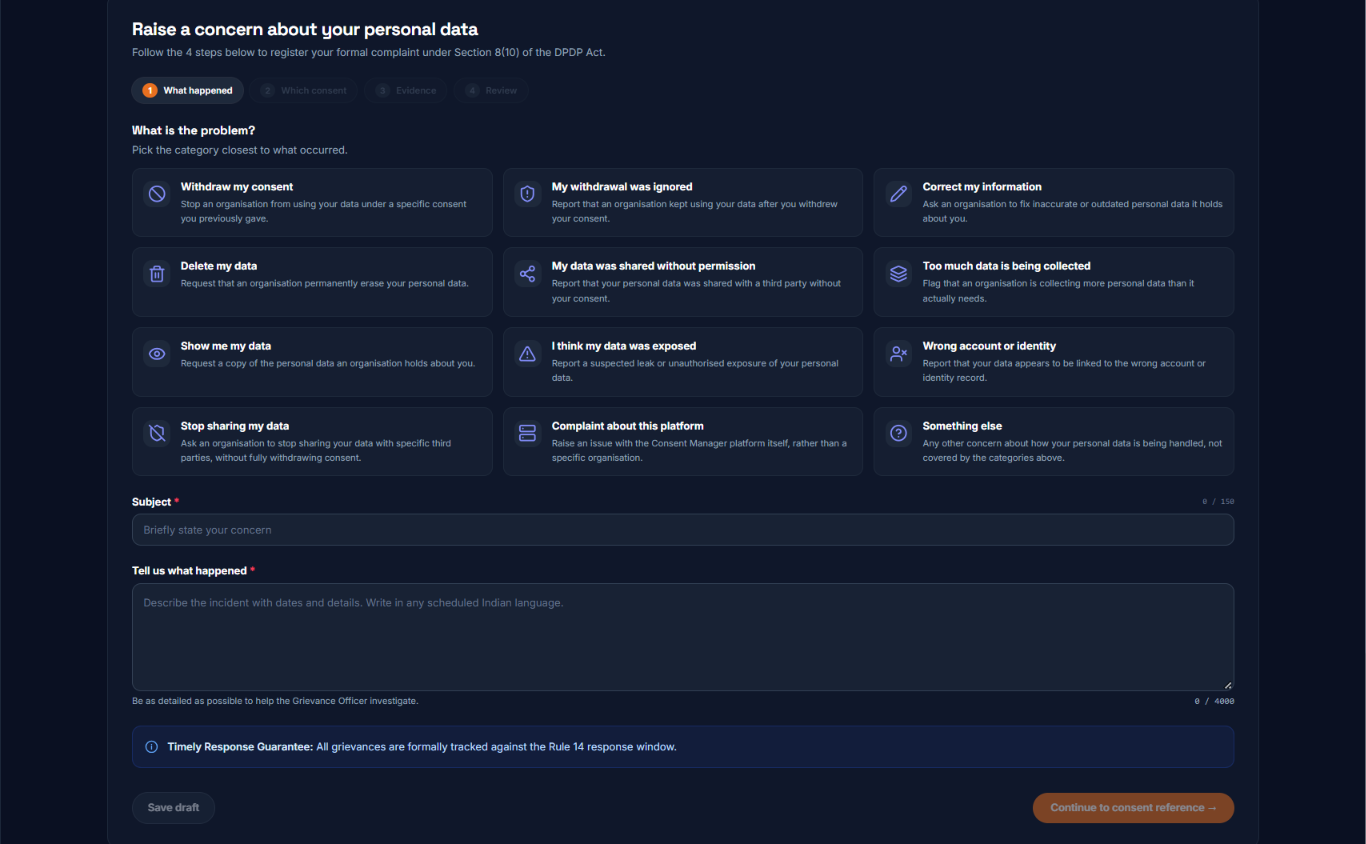
Centralized queue dashboard with intelligent triage
Frontline teams and DPOs manage incoming complaints through multi-parameter filtering, saved views, severity flags, and rapid officer assignments.
- Dynamic filters by category, severity, SLA status, and assigned officer
- Saved quick-filters for unassigned, breached, and personal queues
- Single and bulk ticket reassignment across qualified officers
- Real-time volume metrics and urgency indicators
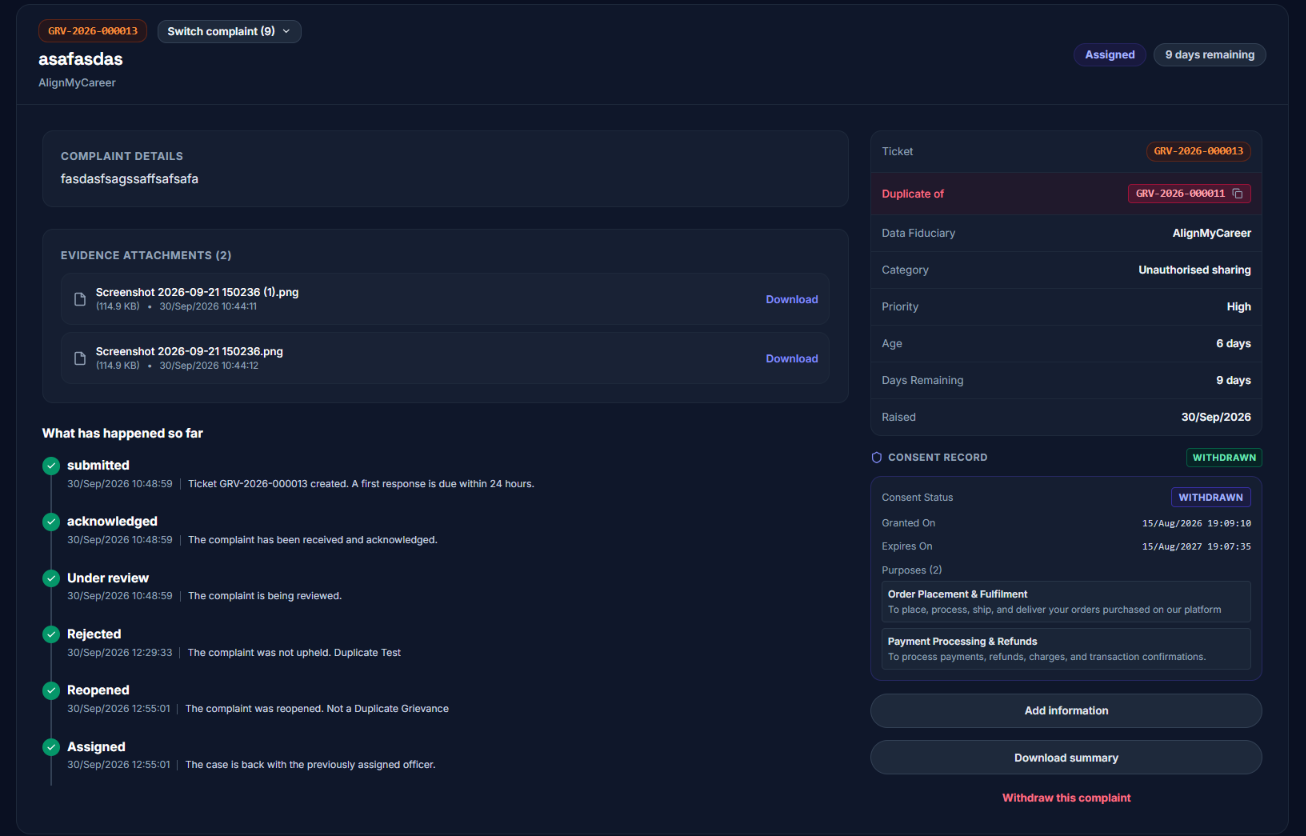
Comprehensive case facts sheet & investigation workspace
Grievance Officers inspect complainant details, review attached evidence, analyze event timelines, and record confidential notes.
- Full case facts card with contact credentials & submission timestamps
- Visual audit timeline displaying chronological lifecycle milestones
- Confidential internal officer notes protected from citizen view
- Direct in-browser inspection of complainant evidence files
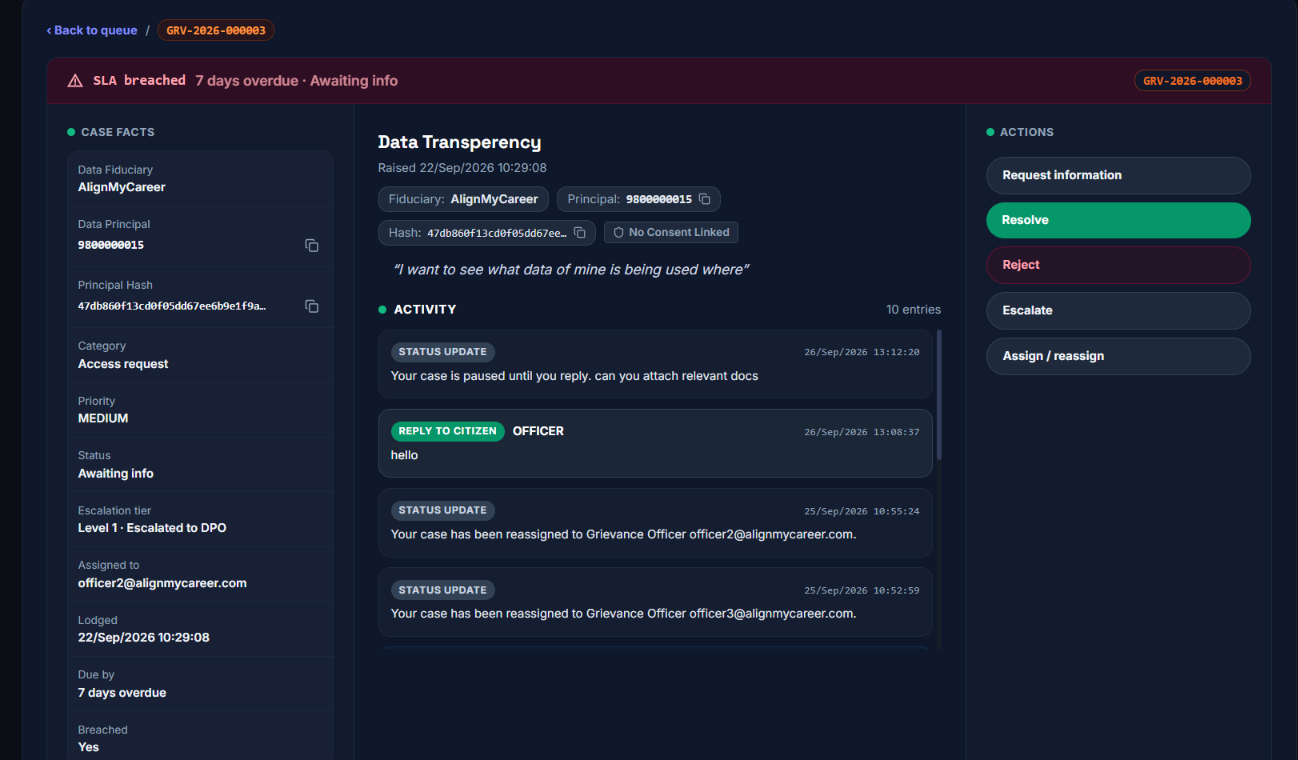
Two-way communication loop with citizen reply banners
When additional facts or documents are necessary, officers issue structured inquiries, and citizens submit replies directly through their tracking screen.
- Official 'Awaiting Information' status transition
- Prominent citizen banner with inquiry context and reply composer
- Secure file upload for supplementary citizen evidence
- Preserves ticket continuity without forcing premature rejections
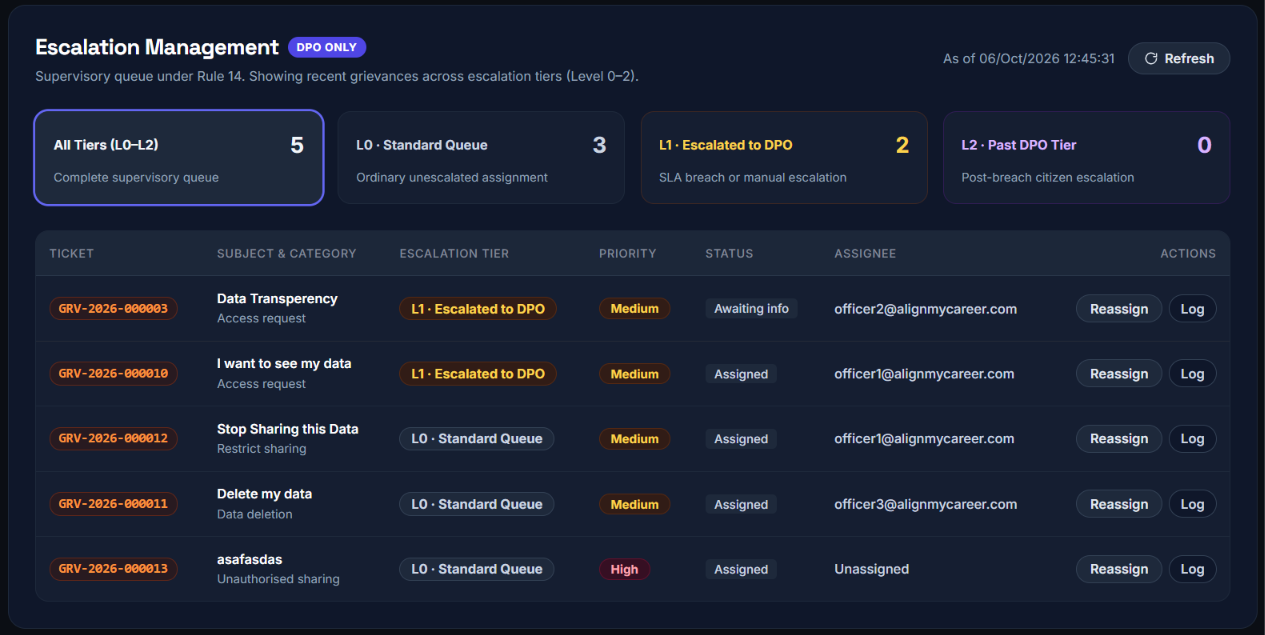
Live statutory SLA countdowns & proactive DPO escalation
Guard against regulatory compliance breaches with real-time countdown badges, amber warning buffers, and automated supervisor escalation.
- Real-time SLA duration timers based on statutory resolution targets
- Clear visual indicators for Normal, Approaching Breach, and Breached
- One-click senior DPO escalation with mandatory reason logging
- DPO override capabilities to reassign stuck investigations
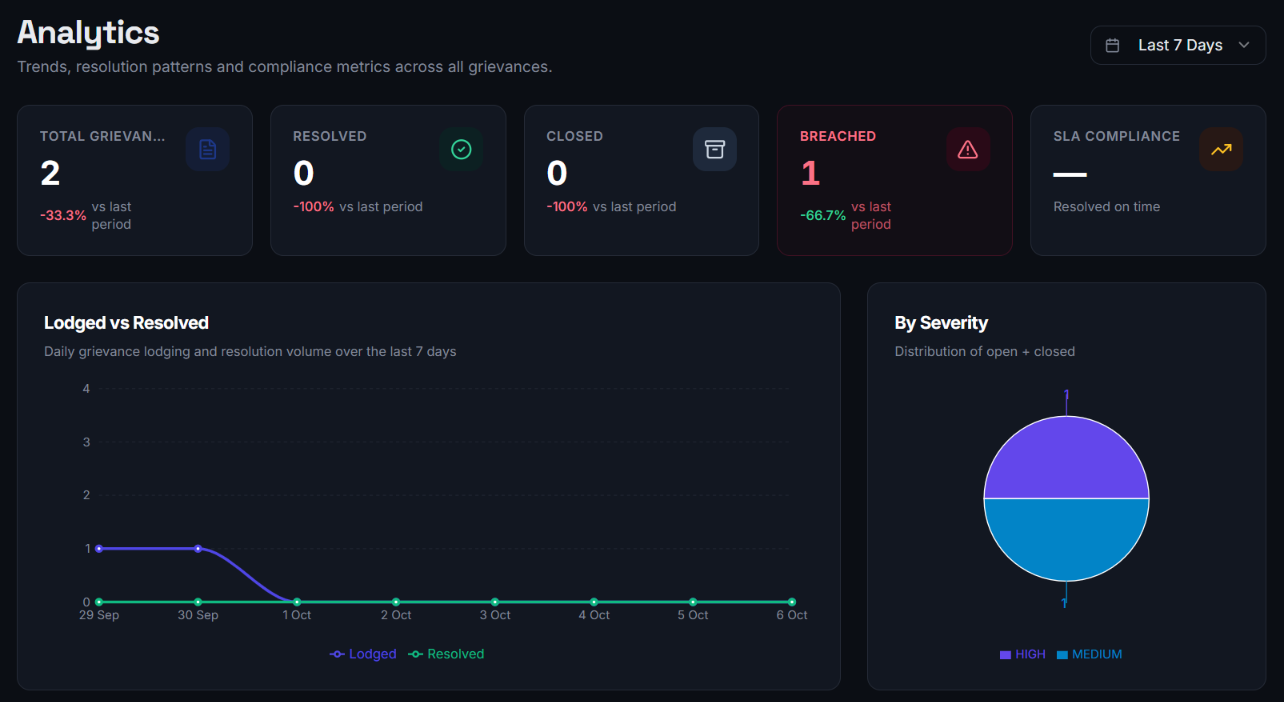
Compliance analytics, SLA velocity & board dossiers
Track statutory compliance velocity, average turnaround times, grievance category distribution, and export comprehensive audit logs for Data Protection Board scrutiny.
- Category distribution & volume trend analytics
- Officer resolution velocity & SLA compliance rates
- Citizen satisfaction & reopen metrics
- Exportable compliance dossiers for regulatory inspection
Multi-lingual complaint intake and real-time status milestone tracking.
Multi-filter triage, saved views, and bulk officer assignments.
Case facts sheets, timeline history, evidence vault, and internal notes.
Automated countdown timers with near-breach alarms and DPO alerts.
Supervisor reassignment and escalated case intervention workflows.
Breakdown of resolution velocity, category trends, and officer metrics.
Questions, answered
What does the DPDP Act 2023 require regarding Grievance Redressal?
Under Section 8(10) and Rule 14, every Data Fiduciary and Consent Manager must establish an easily accessible grievance redressal mechanism. Fiduciaries must acknowledge complaints, investigate concerns within statutory timelines, publish their Grievance Officer details, and maintain defensible records before a citizen may escalate to the Data Protection Board.
Can citizens track complaints without creating a full enterprise account?
Yes. IndiaConsent provides a streamlined Data Principal portal where citizens can authenticate securely via OTP to lodge concerns, inspect real-time progress timelines, and reply to officer questions without complex account setup.
How does the system prevent SLA breaches under DPDP Rule 14?
The platform dynamically assigns resolution deadlines based on grievance categories (e.g. 24h, 72h, or statutory timeframes). Real-time visual SLA indicators alert officers as tickets approach breach thresholds, and automatically surface them on the DPO Escalation Desk for supervisor intervention.
Are internal officer investigation notes visible to the citizen?
No. The system maintains strict separation: internal notes and officer deliberations are visible only to authorized internal personnel (Grievance Officers, DPOs, and Org Admins), while citizen-facing communications and status updates appear in the public milestone timeline.
What happens if a citizen is dissatisfied with the resolution?
Citizens can submit a Reopen request with their rationale directly from the tracking page. The grievance returns to active review under supervisor oversight, ensuring every concern is thoroughly addressed before external regulatory escalation.
Can multiple Grievance Officers and DPOs be provisioned?
Yes. Organizations can provision dedicated teams with distinct roles: Grievance Officers who triage and investigate tickets, Data Protection Officers (DPOs) who oversee compliance and escalations, and Org Admins who manage team memberships.
Modernize your statutory Grievance Redressal program today
Automate citizen rights triage, eliminate SLA breach risks, and satisfy DPDP regulatory mandates with confidence.